Kotlin

hardware-backed security

Building Hardware-Backed Security with Kotlin Multiplatform: From TPM 2.0 to Secure Enclave

Most apps today deal with sensitive data in some form. Tokens, user credentials, payment info, encryption keys. If all of that lives only in app memory, it’s easier to extract than you might think.

That’s why hardware-backed security matters.

Instead of trusting software alone, you let dedicated hardware handle key storage and cryptographic operations. On Android and other devices, that’s often TPM 2.0 (or similar hardware). On Apple devices, it’s the Secure Enclave.

If you’re using Kotlin Multiplatform, you can design this cleanly without duplicating logic across platforms.

Let’s walk through how it actually fits together.

What “Hardware-Backed Security” Really Means

Software-only protection is useful, but it has limits. If malware, root access, or a compromised OS gets in, software-held keys can be exposed more easily.

Hardware-backed systems reduce that risk by keeping keys inside a protected chip or secure execution area. The main app can ask for a cryptographic operation, but it should never see the raw secret.

This is why TPM 2.0 and Secure Enclave are so valuable. They are built to protect keys, verify device state, and make attacks harder even when the surrounding system is not fully trusted.

At a practical level, it means:

  • Keys are generated inside secure hardware
  • They never leave that environment
  • Your app can use them, but can’t extract them

So even if someone reverse engineers your app or dumps memory, the critical material isn’t there.

TPM 2.0 in Practice (Android and Beyond)

TPM 2.0 stands for Trusted Platform Module 2.0. It is a hardware root of trust commonly found on PCs and laptops (on Windows/Linux), and it is used for secure key storage, platform integrity checks, and device attestation.

A TPM can generate keys, store them securely, and perform operations without exposing the private material to normal application memory. It is especially useful for boot integrity, device authentication, and encryption workflows tied to system trust.

Think of TPM 2.0 as a locked vault inside the machine. The app can request a signature or decryption, but it cannot simply open the vault and copy the key.

You usually don’t talk to TPM 2.0 directly on Android. Instead, you go through the Android Keystore system, which uses secure hardware when available.

What you get:

  • Hardware-isolated key storage
  • Built-in enforcement (like requiring biometrics)
  • Protection against key export

From your app’s point of view, you’re just asking the system to generate and use keys. The hardware layer is handled underneath.

Secure Enclave on iOS and macOS

Secure Enclave is Apple’s isolated security subsystem used on Apple devices for protecting sensitive operations. It is commonly used for biometrics, key protection, and secure cryptographic actions.

Like TPM 2.0, it keeps secrets away from normal app memory and the main operating system. The difference is that Secure Enclave is more tightly integrated into Apple’s hardware and software stack, which makes it feel more seamless for iOS and macOS developers.

In practice, Secure Enclave is often the best place to anchor sensitive app secrets on Apple platforms. For user-facing apps, this can support safer authentication, credential storage, and cryptographic signing.

Apple’s Secure Enclave works similarly, but it’s more tightly integrated.

  • Keys are created inside the enclave
  • Biometric checks happen there
  • The OS never exposes raw key material

If you’ve used Face ID or Touch ID to unlock something securely, you’ve already used it.

Where Kotlin Multiplatform Helps

Kotlin Multiplatform is a great choice when you want shared business logic but still need access to platform-specific security features. You can keep your common encryption flow, data models, and validation logic in shared code, then call Android and Apple native APIs for hardware-backed key handling.

This gives you the best of both worlds:

  • Shared security logic in common code.
  • Platform-native key storage on Android and Apple.
  • Less duplicated code across apps.
  • A cleaner path to consistent behavior.

For many teams, Kotlin Multiplatform is the right balance between reuse and platform control.

Recommended architecture

A good design separates responsibilities clearly.

  • Common module: serialization, policy checks, encryption orchestration.
  • Android module: Android Keystore or TPM-backed flows where available.
  • Apple module: Keychain and Secure Enclave-backed APIs where available.
  • Shared interface: a small API that hides platform differences.

This approach keeps your common code simple and testable while allowing each platform to use its strongest security primitive.

Instead of writing separate security flows for Android and iOS, you define a shared contract and implement it per platform.

You’re not trying to abstract the hardware itself. You’re abstracting how your app uses it.

Setting Up the Multiplatform Architecture

To keep our project clean, we use the expect/actual mechanism. We define a common “blueprint” in our shared module and then provide the “real” implementation for each platform.

Note: For simplicity, only Android and iOS are discussed here, but this is not limited to those platforms — we can implement it on other platforms and desktops as well (see the bonus section below).

Define a Common Interface

Start with a simple interface in shared code:

Kotlin
interface SecureKeyManager {
    fun generateKey(alias: String)
    fun encrypt(data: ByteArray): ByteArray
    fun decrypt(data: ByteArray): ByteArray
}

This keeps your business logic independent of platform details.

Android Implementation (Keystore / TPM 2.0-backed)

On Android, this typically goes through the Keystore:

Kotlin
class AndroidSecureKeyManager : SecureKeyManager {

    override fun generateKey(alias: String) {
        val keyGenerator = KeyGenerator.getInstance(
            KeyProperties.KEY_ALGORITHM_AES, "AndroidKeyStore"
        )

        val spec = KeyGenParameterSpec.Builder(
            alias,
            KeyProperties.PURPOSE_ENCRYPT or KeyProperties.PURPOSE_DECRYPT
        )
            .setBlockModes(KeyProperties.BLOCK_MODE_GCM)
            .setEncryptionPaddings(KeyProperties.ENCRYPTION_PADDING_NONE)
            .setUserAuthenticationRequired(true)
            .build()

        keyGenerator.init(spec)
        keyGenerator.generateKey()
    }

    override fun encrypt(data: ByteArray): ByteArray {
        // Real implementation would use Cipher with the stored key
        return data
    }

    override fun decrypt(data: ByteArray): ByteArray {
        return data
    }
}

A few important details:

  • The key is generated inside secure hardware when available
  • You can require biometric auth before use
  • The raw key is never exposed to your code

iOS Implementation (Secure Enclave)

On iOS, you’d use Keychain + Secure Enclave-backed keys.

Kotlin
import platform.Security.*
import platform.Foundation.*

class IOSSecureKeyManager : SecureKeyManager {

    override fun generateKey(alias: String) {
        // Backed by Secure Enclave via iOS Security framework or kotlin native (here we used kotlin native)

        val flags = kSecAccessControlTouchIDAny or kSecAccessControlPrivateKeyUsage
        val accessControl = SecAccessControlCreateWithFlags(
            null, 
            kSecAttrAccessibleWhenUnlockedThisDeviceOnly, 
            flags, 
            null
        )

        val query = mutableMapOf<Any?, Any?>(
            kSecAttrKeyType to kSecAttrKeyTypeECSECPrimeRandom,
            kSecAttrKeySizeInBits to 256,
            kSecAttrTokenID to kSecAttrTokenIDSecureEnclave, // Forces Secure Enclave
            kSecPrivateKeyAttrs to mapOf(
                kSecAttrIsPermanent to true,
                kSecAttrApplicationTag to alias,
                kSecAttrAccessControl to accessControl
            )
        )

        val key = SecKeyCreateRandomKey(query as CFDictionaryRef, null)

        println("Key generated securely: $key")
    }

    override fun encrypt(data: ByteArray): ByteArray {
        return data
    }

    override fun decrypt(data: ByteArray): ByteArray {
        return data
    }
}

The key here is kSecAttrTokenIDSecureEnclave. This tells iOS: “Don’t just store this in a database; burn this key into the hardware. 

In a real app, this bridges into Swift/Objective-C APIs. Kotlin/Native calls into those under the hood.

Wiring It Together with expect/actual

Kotlin Multiplatform lets you plug in platform-specific implementations cleanly.

Shared code:

Kotlin
expect class PlatformSecureKeyManager() : SecureKeyManager

Android:

Kotlin
actual class PlatformSecureKeyManager actual constructor() :
    AndroidSecureKeyManager()

iOS:

Kotlin
actual class PlatformSecureKeyManager actual constructor() :
    IOSSecureKeyManager()

Now the rest of your app just depends on SecureKeyManager.

Bonus: Implementing TPM 2.0 (Windows/Desktop)

For Windows or Linux desktop targets, Kotlin Multiplatform uses Kotlin/Native to talk to system C-libraries. On Windows, we typically interact with the NCrypt (Next Generation Cryptography) library to access the TPM 2.0.

The Windows Implementation

In your desktopMain or mingwMain, you would use cinterop to call the Windows CNG (Cryptography Next Generation) API:

Kotlin
import kotlinx.cinterop.*
import platform.windows.*

class WindowsTPMProvider : SecureKeyManager {

    // Using the Microsoft Platform Crypto Provider specifically targets the TPM
    private val MS_PLATFORM_CRYPTO_PROVIDER = "Microsoft Platform Crypto Provider"

    override fun generateKey(alias: String) {
        memScoped {
            val hProvider = alloc<NCRYPT_PROV_HANDLEVar>()
            val hKey = alloc<NCRYPT_KEY_HANDLEVar>()

            // 1. Open the TPM Storage Provider
            NCryptOpenStorageProvider(hProvider.ptr, MS_PLATFORM_CRYPTO_PROVIDER, 0)

            // 2. Create a new RSA or ECC key persisted in hardware
            NCryptCreatePersistedKey(
                hProvider.value,
                hKey.ptr,
                BCRYPT_RSA_ALGORITHM, // You can also use BCRYPT_ECDSA_P256_ALGORITHM
                alias,
                0,
                0
            )

            // 3. Finalize the key to "burn" it into the TPM
            NCryptFinalizeKey(hKey.value, 0)

            // Clean up handles
            NCryptFreeObject(hKey.value)
            NCryptFreeObject(hProvider.value)
        }
    }

    override fun encrypt(data: ByteArray): ByteArray {
        // Implementation would involve NCryptOpenKey using the alias
        // followed by NCryptEncrypt
        // For hardware-backed keys, the TPM handles the actual math
        return todo("NCryptEncrypt implementation")
    }

    override fun decrypt(data: ByteArray): ByteArray {
        // Implementation would involve NCryptOpenKey using the alias
        // followed by NCryptDecrypt
        return todo("NCryptDecrypt implementation")
    }
}
  • The Provider: By using MS_PLATFORM_CRYPTO_PROVIDER, you are explicitly telling Windows to bypass the software-based providers and use the TPM 2.0 chip. If the device lacks a TPM, this call will fail, allowing you to handle the error gracefully.
  • NCryptFinalizeKey: In the Windows CNG (Cryptography Next Generation) API, a key isn’t “real” until you finalize it. This is the moment the TPM 2.0 generates the key material internally.
  • Memory Management: Since this is Kotlin Multiplatform targeting Windows (Native), we use memScoped and alloc. This ensures that pointers used for Windows C-headers are cleaned up properly, preventing memory leaks in your security layer.

Where This Is Actually Useful

This setup shows up in a few common places:

  • Storing auth tokens securely
  • Encrypting local database values
  • Managing private keys for end-to-end encryption
  • Adding biometric protection to sensitive actions

You don’t need to over-engineer it. Even using hardware-backed storage for one critical key is a big improvement.

Things That Trip People Up

Some common mistakes:

  • Assuming all devices have hardware-backed storage
  • Forgetting to handle fallback paths
  • Treating encryption as useful without secure key storage
  • Not testing biometric-required flows properly

Also worth noting: emulators don’t behave the same as real devices here.

A Few Practical Tips

  • Always prefer hardware-backed keys when available
  • Require user authentication for sensitive operations
  • Don’t cache decrypted data longer than needed
  • Keep your abstraction small and focused

You don’t need a huge framework. Just a clean boundary and correct usage.

Conclusion

You don’t interact with TPM 2.0 or Secure Enclave directly most of the time. The platform APIs handle that. Your job is to use them correctly and structure your code so it stays maintainable.

That’s where Kotlin Multiplatform helps. You define the contract once, plug in the platform specifics, and keep the rest of your app clean.

If you’re already sharing business logic across platforms, adding this layer is a natural next step.
Kotlin Multiplatform vs Kotlin Native

Kotlin Multiplatform vs Kotlin Native: What’s the Real Difference in 2026?

If you’ve been exploring cross-platform development with Kotlin, you’ve probably come across the debate: Kotlin Multiplatform vs Kotlin Native. At first glance, they can feel similar. Both let you use Kotlin beyond Android. Both promise code reuse. But they solve different problems.

In this guide, we’ll break down Kotlin Multiplatform & Kotlin Native to help you understand the real-world differences in 2026.

First, What Is Kotlin?

Kotlin is a modern programming language created by JetBrains. It’s concise, safe, and fully interoperable with Java.

Kotlin
fun greet(name: String): String {
    return "Hello, $name!"
}

fun main() {
    println(greet("amol"))
}

What’s happening here:

  • fun defines a function
  • name: String means the function expects a text input
  • The function returns a greeting string
  • Kotlin automatically handles many things like null safety and type inference

Now let’s move into the real topic.

What Is Kotlin Native?

Kotlin Native is a technology that compiles Kotlin code directly into native machine code.

That means:

  • No JVM (Java Virtual Machine)
  • No Android runtime
  • Runs directly on platforms like iOS, macOS, Linux, Windows

Simple Kotlin Native Example

Kotlin
import platform.Foundation.*

fun main() {
    println("Hello from Kotlin Native!")
}

This code can run as a standalone native binary.

Key Idea

Kotlin Native is about how your code runs.

It focuses on:

  • Performance
  • Native platform access
  • Direct compilation

What Is Kotlin Multiplatform?

Kotlin Multiplatform (KMP) is a development approach.

It lets you:

  • Share code across platforms (Android, iOS, Web, Backend)
  • Keep platform-specific code where needed

Example Structure

Kotlin
shared/
├── commonMain/kotlin/     // Shared code
├── androidMain/kotlin/    // Android extras
└── iosMain/kotlin/        // iOS extras
Kotlin
// Shared code
expect fun platformName(): String

fun greet(): String {
    return "Hello from ${platformName()}"
}
Kotlin
// Android implementation
actual fun platformName(): String = "Android"
Kotlin
// iOS implementation
actual fun platformName(): String = "iOS"

What’s happening here:

  • expect declares a function in shared code
  • actual provides platform-specific implementations
  • You write logic once, customize where needed

Key Idea

Kotlin Multiplatform is about how you structure your codebase.

Kotlin Multiplatform vs Kotlin Native: Core Difference

Here’s the simplest way to understand it:

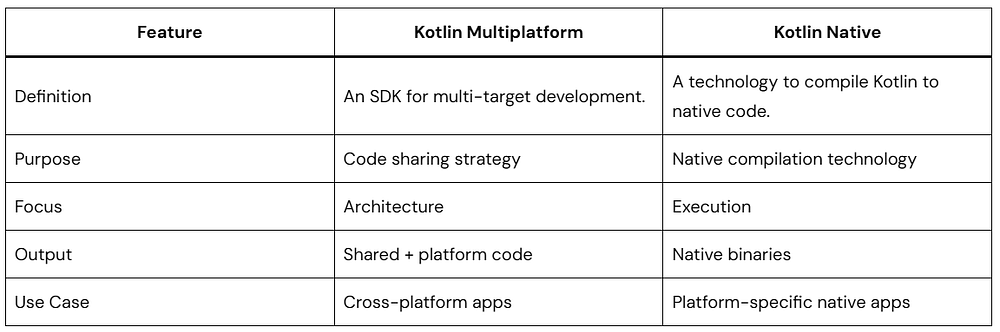
  • Kotlin Native = a compiler/runtime technology
  • Kotlin Multiplatform = a development framework/approach

They are not competitors. They work together.

How They Work Together

When comparing Kotlin Multiplatform vs Kotlin Native, it’s important to know this:

Kotlin Multiplatform uses Kotlin Native under the hood for iOS and other native targets.

So:

  • You write shared code using Kotlin Multiplatform
  • That shared code gets compiled using Kotlin Native (for iOS, etc.)

Real-World Example

Imagine you’re building a mobile app:

With Kotlin Multiplatform:

  • Business logic (API calls, validation) is shared
  • UI is written separately (SwiftUI for iOS, Jetpack Compose for Android)

With Kotlin Native:

  • The shared code gets compiled into native iOS binaries

Key Differences Table

When Should You Use Kotlin Multiplatform?

Choose Kotlin Multiplatform if:

  • You want to share business logic across platforms
  • You’re building Android + iOS apps
  • You want flexibility in UI development
  • You care about reducing duplicate code

Example Use Cases:

  • Fintech apps
  • E-commerce apps
  • APIs and SDKs

When Should You Use Kotlin Native?

Choose Kotlin Native if:

  • You need a fully native application

You are building:

  • CLI tools
  • System-level software
  • Performance-critical modules
  • You don’t need cross-platform sharing

Performance: Kotlin Multiplatform vs Kotlin Native

This is a common question.

  • Kotlin Native produces true native binaries, so performance is excellent
  • Kotlin Multiplatform inherits that performance when targeting native platforms

However:

  • KMP adds a layer of architecture complexity
  • Native-only projects may be simpler for small apps

Developer Experience in 2026

Things have improved a lot.

Kotlin Multiplatform:

  • Better tooling in Android Studio
  • Improved iOS integration
  • Faster builds
  • More stable libraries

Kotlin Native:

  • Improved memory management (no more freezing issues like early versions)
  • Better debugging tools

Common Misconception

Many developers think:

“Kotlin Multiplatform & Kotlin Native is a choice between two competing tools.”

That’s not true.

You don’t choose one over the other…
You use them together..!

A Simple Mental Model

Think of it like this:

  • Kotlin Multiplatform = the blueprint
  • Kotlin Native = the engine that runs part of that blueprint

FAQ

Q: What is the difference between Kotlin Multiplatform and Kotlin Native?
Kotlin Multiplatform is a framework for sharing code across platforms, while Kotlin Native is a compiler that turns Kotlin code into native binaries. Kotlin Multiplatform often uses Kotlin Native for iOS and other native targets.

Q: Can Kotlin Multiplatform work without Kotlin Native?
Partially. It can target JVM and JS without Kotlin Native, but for iOS or native platforms, Kotlin Native is required.

Q: Which is better in 2026?
Neither is “better.” Kotlin Multiplatform is the higher-level solution, and Kotlin Native is part of how it works.

Conclusion

The debate around Kotlin Multiplatform vs Kotlin Native often comes from misunderstanding their roles.

If you remember just one thing, let it be this:

  • Kotlin Multiplatform helps you share code
  • Kotlin Native helps you run code natively

Together, they form a powerful toolkit for modern app development in 2026.

kotlin native

What Is Kotlin Native? A Complete Beginner’s Guide to Cross-Platform Power

If you’ve ever wanted to write code once and run it across multiple platforms without dragging along a heavy runtime, Kotlin Native is worth a look. It lets you take Kotlin beyond the JVM and compile it into real native binaries. That changes how your apps start, run, and scale across platforms. Let’s break it...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
Kotlin Native CInterop

Kotlin Native CInterop Explained: Seamlessly Call C Code Like a Pro

If you’ve ever needed to use an existing C library in a Kotlin project, you’ve probably run into the gap between modern Kotlin and low-level native code. That’s where Kotlin Native CInterop comes in. This guide breaks it down in a practical way. No fluff, just what you need to understand how it works and...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
Compose Multiplatform

Compose Multiplatform (CMP) in Production: The Complete Technical Guide for Android, iOS & Web

If you’ve been in the mobile and cross-platform world lately, you’ve probably heard a lot about Compose Multiplatform (CMP). It’s one of the fastest-growing ways to build apps that run on Android, iOS and the Web using a single shared UI approach. But what exactly is CMP? And why are developers increasingly choosing it over...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
Factory Pattern Simplify Complex Object Creation

How Does the Factory Pattern Simplify Complex Object Creation in Modern Applications?

Creating objects sounds simple at first. You call a constructor, pass a few values, and move on.

But as applications grow, object creation often becomes messy.

You start seeing:

  • Too many if-else or when blocks
  • Classes tightly coupled to concrete implementations
  • Code that’s hard to test, extend, or understand

This is exactly where the Factory Pattern Simplify Complex Object Creation problem in modern applications.

Let’s break it down in a clear and practical way.

What Is the Factory Pattern?

The Factory Pattern is a creational design pattern that handles object creation for you.

Instead of creating objects directly using constructors, you delegate that responsibility to a factory.

In simple terms:

A factory decides which object to create and how to create it.

Your main code just asks for an object and uses it. It doesn’t care about the details.

This separation is what makes the Factory Pattern Simplify Complex Object Creation so effective.

Why Object Creation Becomes Complex

In real-world applications, object creation often depends on:

  • User input
  • Configuration files
  • API responses
  • Environment (development, testing, production)

Example without a factory:

Kotlin
val paymentProcessor = when (paymentType) {
    "CARD" -> CardPaymentProcessor()
    "UPI" -> UpiPaymentProcessor()
    "WALLET" -> WalletPaymentProcessor()
    else -> throw IllegalArgumentException("Invalid payment type")
}

Now imagine this logic repeated across multiple files.

Problems appear quickly:

  • Code duplication
  • Hard-to-maintain logic
  • Difficult testing
  • Violations of the Single Responsibility Principle

This is why developers rely on patterns that simplify complex object creation.

How the Factory Pattern Helps

The Factory Pattern solves these issues by:

  • Centralizing object creation
  • Reducing tight coupling
  • Making code easier to extend
  • Improving testability

Most importantly, it lets your business logic focus on what to do, not how objects are created.

That’s the real power behind Factory Pattern Simplify Complex Object Creation.

A Simple Kotlin Example

Define a Common Interface

Kotlin
interface Notification {
    fun send(message: String)
}

This interface represents a notification system.

Create Concrete Implementations

Kotlin
class EmailNotification : Notification {
    override fun send(message: String) {
        println("Sending Email: $message")
    }
}

class SmsNotification : Notification {
    override fun send(message: String) {
        println("Sending SMS: $message")
    }
}

class PushNotification : Notification {
    override fun send(message: String) {
        println("Sending Push Notification: $message")
    }
}

Each class has its own behavior but follows the same contract.

Create the Factory

Kotlin
object NotificationFactory {

    fun create(type: String): Notification {
        return when (type.uppercase()) {
            "EMAIL" -> EmailNotification()
            "SMS" -> SmsNotification()
            "PUSH" -> PushNotification()
            else -> throw IllegalArgumentException("Unknown notification type")
        }
    }
}

This is the heart of the Factory Pattern.

The factory:

  • Knows which object to create
  • Hides creation logic from the rest of the app

Use the Factory

Kotlin
val notification = NotificationFactory.create("EMAIL")
notification.send("Welcome to our platform!")

That’s it.

The calling code:

  • Does not know about concrete classes
  • Does not change if new notification types are added

This is how the Factory Pattern Simplify Complex Object Creation in Kotlin applications.

Why Kotlin Works So Well with Factory Pattern

Kotlin makes the Factory Pattern even cleaner because of:

  • object keyword for singletons
  • when expressions
  • Strong type safety
  • Concise syntax

Factories in Kotlin are:

  • Easy to read
  • Hard to misuse
  • Simple to test

This makes Kotlin a great fit for modern, scalable architecture.

Real-World Use Cases

You’ll see the Factory Pattern used in:

  • Database connection creation
  • Payment gateways
  • Logging frameworks
  • UI component generation
  • API client creation

Anywhere object creation depends on conditions, the Factory Pattern Simplify Complex Object Creation effectively.

Factory Pattern and Clean Architecture

From an architectural perspective, the Factory Pattern supports:

  • Loose coupling
  • Open/Closed Principle
  • Single Responsibility Principle

Your system becomes:

  • Easier to extend
  • Safer to modify
  • More readable for new developers

Common Mistakes to Avoid

Even with factories, mistakes happen.

Avoid:

  • Putting business logic inside the factory
  • Creating overly complex factories
  • Ignoring interfaces

A factory should only create objects, nothing more.

When Should You Use the Factory Pattern?

Use it when:

  • Object creation logic is complex
  • You expect future extensions
  • You want cleaner, testable code

Avoid it for:

  • Very small or one-off objects
  • Simple scripts

Conclusion

The Factory Pattern Simplify Complex Object Creation by separating object creation from object usage.

It keeps your code:

  • Clean
  • Flexible
  • Easy to maintain

In modern Kotlin applications, this pattern is not just useful. It’s often essential.

If you’re building scalable systems, learning and applying the Factory Pattern is a smart investment in code quality and long-term success.

Use Case Patterns

Mastering Use Case Patterns: A Practical Guide for Modern Software Design

Modern software design isn’t just about writing code that works; it’s about writing code that’s maintainable, scalable, and easy to understand. One way to achieve this is by using Use Case Patterns — a structured approach to modeling software functionality based on real-world user interactions. In this guide, we’ll break down everything you need to know about...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
Repository Pattern

How the Repository Pattern Makes Code Easier to Test, Maintain, and Scale

Software projects rarely stay small. Features grow, requirements change, and teams expand. When data access logic is tightly coupled with business logic, even a simple update can break multiple parts of the system. This is where the Repository Pattern becomes extremely valuable. In this blog, we’ll explain the Repository Pattern in a clear and beginner-friendly...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
Kotlin Sequences

Kotlin Sequences or Java Streams? A Complete Guide for Modern Developers

If you’ve ever worked with collections in Kotlin or Java, you’ve probably heard about Kotlin Sequences and Java Streams. Both are powerful tools for handling large amounts of data in a clean, functional style. But when should you use one over the other? And what’s the real difference between them?

This guide breaks it all down in simple way — no jargon overload. By the end, you’ll know exactly when to reach for Kotlin Sequences or Java Streams in your projects.

Why Do We Even Need Sequences or Streams?

Collections like List and Set are everywhere. But looping through them with for or while can quickly become messy, especially when you want to:

  • Filter elements
  • Map values
  • Reduce results into a single outcome

This is where lazy evaluation comes in. Instead of processing all elements up front, sequences and streams let you chain operations in a pipeline. The work only happens when you actually need the result. That means cleaner code and often better performance.

Kotlin Sequences: Lazy by Design

Kotlin’s Sequence is basically a wrapper around collections that delays execution until the final result is requested.

Filtering and Mapping with Sequences

Kotlin
fun main() {
    val numbers = listOf(1, 2, 3, 4, 5)

    val result = numbers.asSequence()
        .filter { it % 2 == 1 }   // Keep odd numbers
        .map { it * it }          // Square them
        .toList()                 // Trigger evaluation

    println(result) // [1, 9, 25]
}

Here,

  • .asSequence() converts the list into a sequence.
  • filter and map are chained, but nothing actually runs yet.
  • .toList() triggers evaluation, so all steps run in a pipeline.

Key takeaway: Sequences process elements one by one, not stage by stage. That makes them memory-efficient for large datasets.

Java Streams: Functional Power in Java

Java introduced Stream in Java 8, giving developers a way to work with collections functionally.

Filtering and Mapping with Streams

Java
import java.util.*;
import java.util.stream.*;

public class StreamExample {
    public static void main(String[] args) {

        List<Integer> numbers = Arrays.asList(1, 2, 3, 4, 5);

        List<Integer> result = numbers.stream()
            .filter(n -> n % 2 == 1)  // Keep odd numbers
            .map(n -> n * n)          // Square them
            .toList();                // Collect into a list

        System.out.println(result);   // [1, 9, 25]

    }
}

How It Works

  • .stream() converts the collection into a stream.
  • Operations like filter and map are chained.
  • .toList() (or .collect(Collectors.toList()) in older Java versions) triggers evaluation.

Streams are also lazy, just like Kotlin Sequences. But they come with a big advantage: parallel processing.

Kotlin Sequences vs Java Streams: Key Differences

Here’s a side-by-side comparison of Kotlin Sequences or Java Streams:

When to Use Kotlin Sequences

  • You’re writing Kotlin-first code.
  • You want simple lazy evaluation.
  • You’re processing large collections where memory efficiency matters.
  • You don’t need parallel execution.

Example: processing thousands of lines from a text file efficiently.

When to Use Java Streams

  • You’re in a Java-based project (or interoperating with Java).
  • You want parallel execution to speed up heavy operations.
  • You’re working with Java libraries that already return streams.

Example: data crunching across millions of records using parallelStream().

Which Should You Choose?

If you’re in Kotlin, stick with Kotlin Sequences. They integrate beautifully with the language and make your code feel natural.

If you’re in Java or need parallel execution, Java Streams are the way to go.

And remember: it’s not about one being “better” than the other — it’s about choosing the right tool for your context.

Conclusion

When it comes to Kotlin Sequences or Java Streams, the choice boils down to your project’s ecosystem and performance needs. Both give you lazy, functional pipelines that make code cleaner and more maintainable.

  • Kotlin developers → Sequences
  • Java developers or parallel workloads → Streams

Now you know when to use each one, and you’ve seen them in action with real examples. So the next time you need to process collections, you won’t just write a loop — you’ll reach for the right tool and make your code shine.

Doubly Linked List in Kotlin

Doubly Linked List in Kotlin: Real-World Use Cases and Code Snippets

When working with data structures in Kotlin, arrays and lists often come to mind first. They’re built-in, simple, and cover most scenarios. But sometimes you need more control over how elements are connected, inserted, or removed. That’s where a Doubly Linked List in Kotlin shines. In this blog, we’ll explore what a doubly linked list...

Membership Required

You must be a member to access this content.

View Membership Levels

Already a member? Log in here
error: Content is protected !!